Cyberattacks Up 48% in September 2026, Europe Up 61%: Check Point Report
Check Point: cyberattacks rose 48% year over year in September 2026 and 61% in Europe, with ransomware up 53%. Key takeaways for businesses.
News & analysis
Incidents, vulnerabilities, regulations (NIS2, DORA, KSC) and practical guides — we write about what really changes security for businesses.
Check Point: cyberattacks rose 48% year over year in September 2026 and 61% in Europe, with ransomware up 53%. Key takeaways for businesses.
CyberXero uses 51 AI agents to break into WordPress sites and infrastructure. Poland is its No. 2 target, with 284 government domains scanned.
FBI warns the FortiBleed campaign has hijacked 86,000+ Fortinet FortiGate firewalls and VPNs, passing access to ransomware gangs. 7 steps to take now.
After the MyDr and Medyc data breaches, Poland's government will publicly name companies that fail to secure data. What it means for boards.
Hackers are exploiting CVE-2026-21589 in Jira, Confluence and Bitbucket Data Center to steal crowd.properties credentials. Here's what to do now.
CVE-2026-21589 (CVSS 9.3) affects eight Atlassian Data Center products; Cloud is already patched. Fixed versions and what to do if you can't patch yet.
Attackers hijacked a third-party ASOS messaging platform and pushed a threat to app users. Names and contact details may be exposed. What's the lesson?
Attackers spent 10 days pulling names, addresses and CPR numbers via a partner firm's legitimate access. What it teaches about third-party access risk.
CVE-2026-88779 in SAML-enabled NetScaler ADC and Gateway was exploited before a patch. Attackers inject commands via the username field. Patch now.
Over 600,000 customers and about 6 TB of invoices exposed. The facts on the Fakturownia breach and how to limit the damage, including notifying UODO.
CVE-2026-104286 (CVSS 9.8) lets unauthenticated attackers write arbitrary files on FortiMail and is actively exploited. See patches and mitigations.
Modern LLMs are hitting a memory wall. TurboQuant's vector compression shrinks the KV cache fivefold without sacrificing model intelligence.
litellm, pulled 97M times a month, shipped malware that ran without an import. Only its own bug stopped silent theft of SSH keys and cloud credentials.
Poland's Digital Affairs Minister recommends phone antivirus. We explain what Android antivirus apps can and can't do, and whether you really need one.
A hacker tricked Anthropic's Claude and OpenAI's ChatGPT into helping steal 150 GB of Mexican government data. Here's how the AI jailbreak worked.
Mandatory KSeF is here. Learn how phantom invoices and fake tax office emails target Polish businesses, and how to protect your company from fraud.
Tesla's Mixed-Precision Bridge patent application brings 32-bit AI precision to cheap 8-bit chips. What it means for FSD, Optimus and edge AI.
A complete roundup of the best free, open source penetration testing tools for 2026, from operating systems and web scanners to advanced code analysis.
In-house SOC vs. SOCaaS: costs, TCO and ROI compared, a case study, and NIS2's impact on IT budgets. Why the hybrid model wins in 2026.
A practical guide to SIEM transformation: data normalization, the Pyramid of Pain and Detection as Code. Learn to detect behaviors, not just signatures.
Poland published the mObywatel app's source code, but login walls, right-click blocks and missing backend code turned openness into a facade.
Eight critical Chrome zero-days in one year. How APT groups weaponized the V8 engine, and why the sandbox alone is no longer enough in 2025.
AI isn't only about medicine and convenience. Malicious LLMs like WormGPT and KawaiiGPT are democratizing cybercrime and crafting flawless scams.
Industry 4.0 has ended the era of isolated factories. Learn how IEC 62443 upends traditional thinking about protecting critical infrastructure.
Can AI have trauma? Researchers put ChatGPT, Gemini and Grok through therapy sessions. The result: synthetic psychopathology and a new jailbreak risk.
An analysis of 100 trillion tokens debunks AI myths: roleplay beats office productivity, and users stick to models like Cinderella's glass slipper.
Why did RAM prices skyrocket in 2025? It's not just AI. Inside the silicon physics, Samsung's strategy and the end of Windows 10.
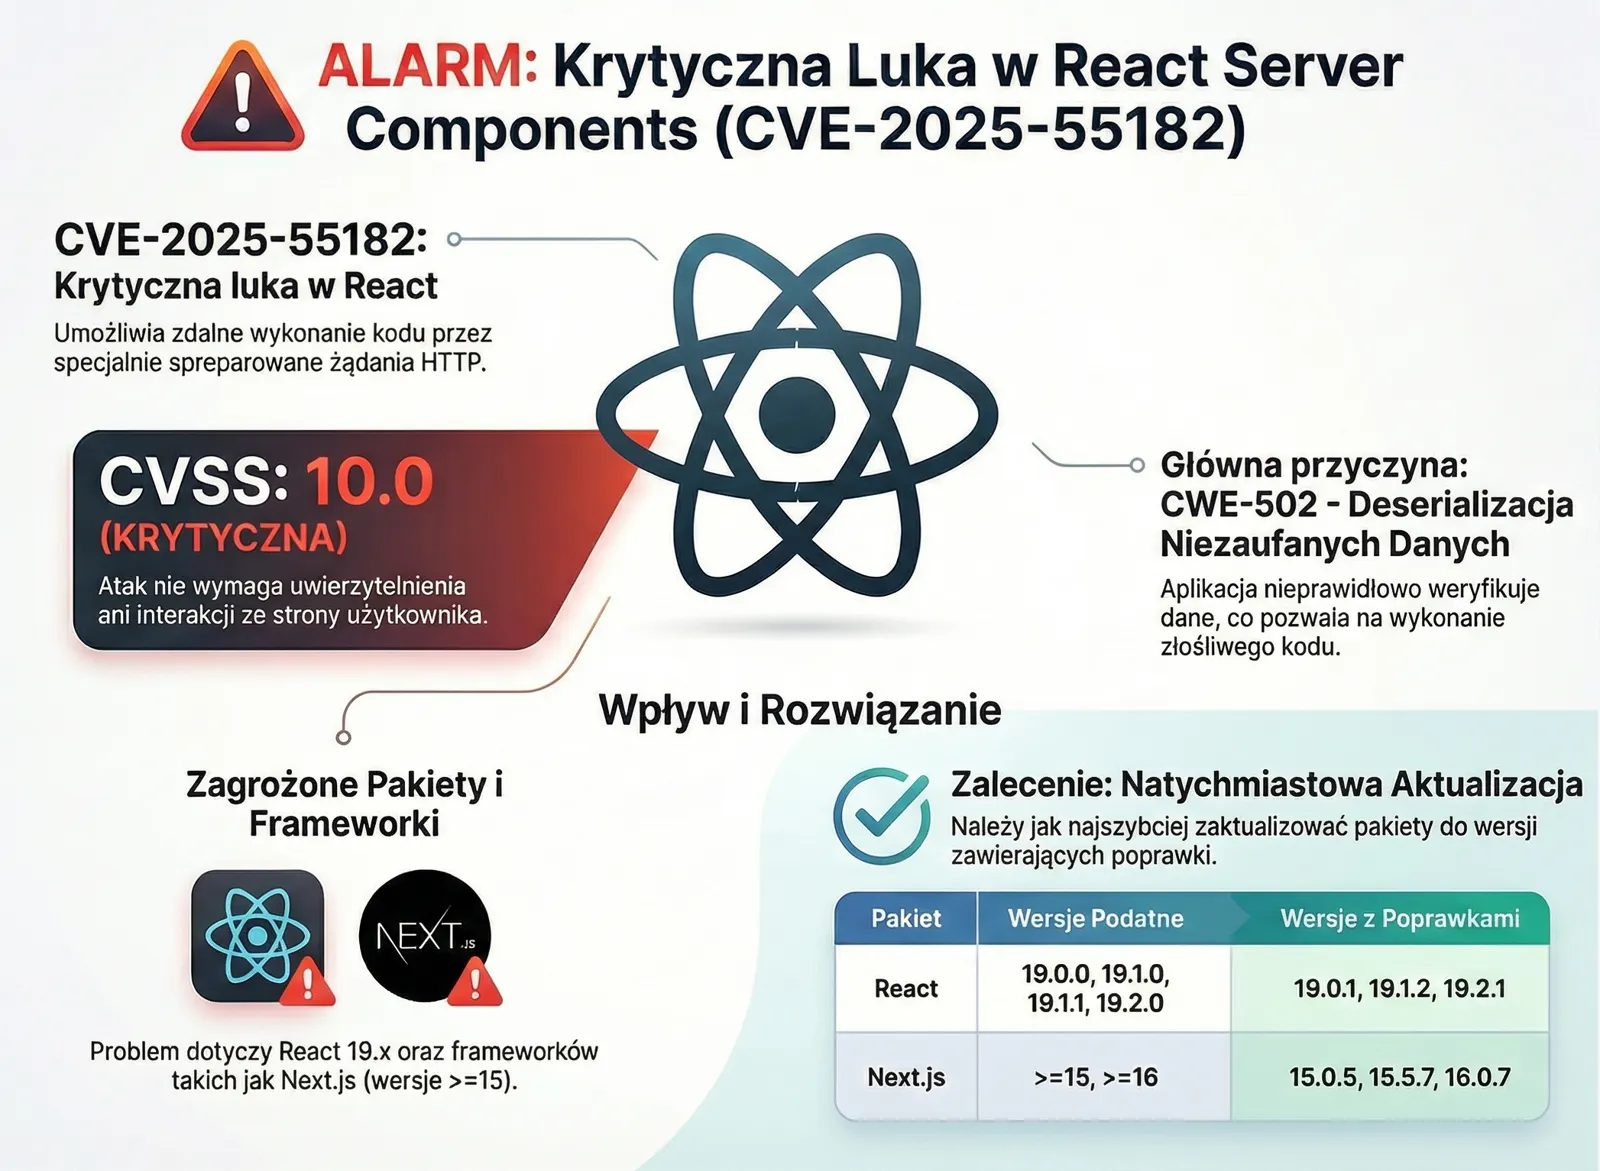
Patched the CVSS 10.0 React2Shell flaw? You're not done. New React Server Components bugs bring DoS and source code exposure to Next.js apps.
Poland's cyber defense has two faces: the new cyber.gov.pl portal with free tools for citizens, and openly acknowledged offensive cyberweapons.
The Dom Development cyberattack exposed PESEL numbers, salaries and children's data. What leaked, what it means, and how to protect yourself now.
Poland plans record spending to fight disinformation in 2026. Inside the government's strategy, from a huge awareness campaign to defending NASK.
Tor is replacing AES-CTR relay encryption with Counter Galois Onion (CGO). What changes, why tagging attacks fail, and where it's 3x faster.
Researchers show how delivery receipts in WhatsApp and Signal let anyone with your number track your screen activity and location and drain your battery.
Running Next.js? React2Shell (CVE-2025-55182) enables remote code execution. Here's how Vercel responded and what you need to patch right now.
Your 2026 guide to the Security Operations Center: team structure, SIEM/XDR/SOAR, NIS2 requirements, deployment models and AI. For CISOs and IT leaders.
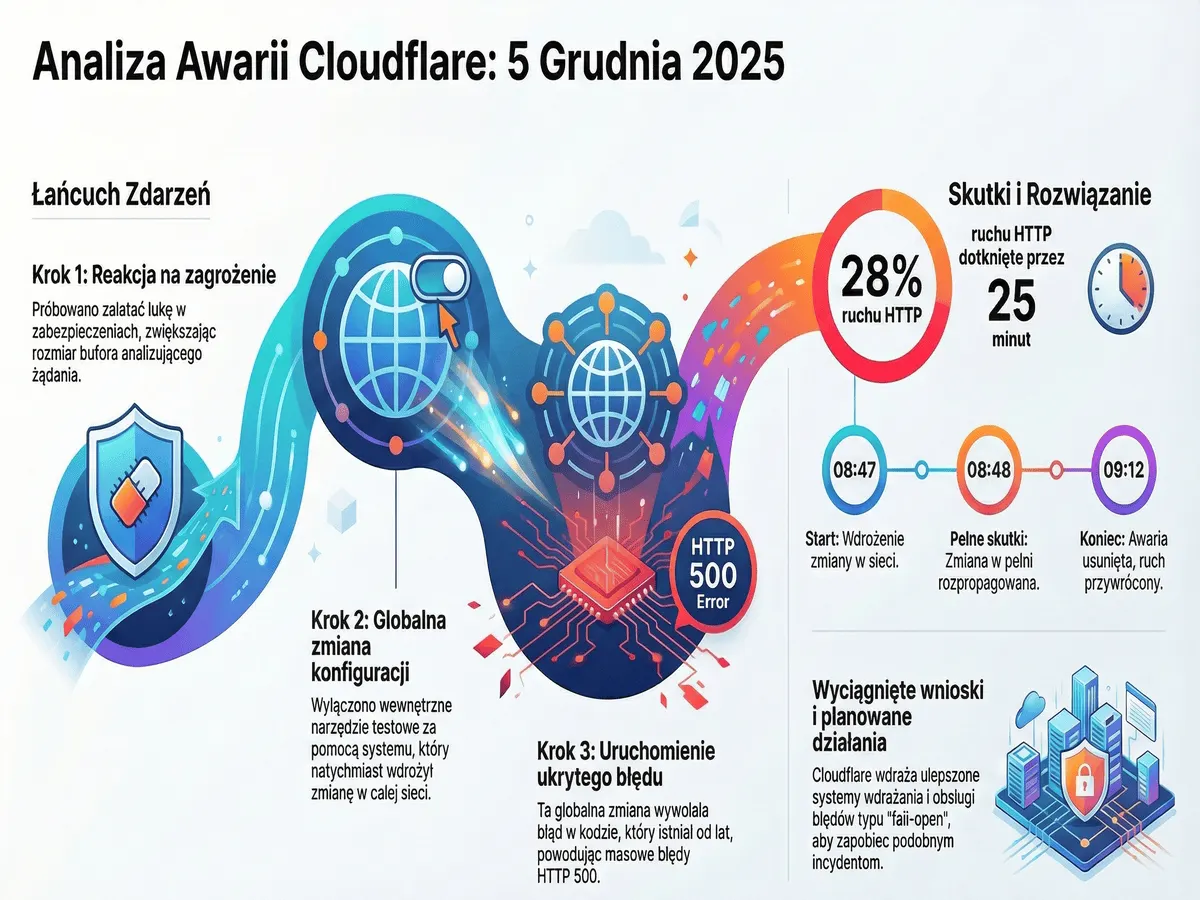
Cloudflare's 25-minute outage on December 5, 2025, explained: a React CVE fix, a WAF buffer change and a fatal Lua nil-value bug.
Agentic AI is rewriting the threat landscape. Learn how Claude Code was weaponized by APT groups like GTG-1002 and why Vibe Hacking matters.
On December 5, Cloudflare stumbled again, taking Zoom and Fortnite down with it. Plus: DownDetectorDownDetector is real, not a meme.
A critical flaw in React Server Components (CVE-2025-55182) enables unauthenticated remote code execution and scored a maximum CVSS 10.0. Patch now.
Over 600,000 incident reports. We break down NASK and police data on deadly TikTok challenges, Roblox scams, and Poland's sexting legal trap.
Everyone's feeling the vibe, but nobody reads the code. We look at vibe coding, the rise of slopsquatting, and how AI quietly weakens app security.
75,000 posts, a geolocated window view and... a photo of a dog. See how OSINT techniques unmasked the online hater behind "Morgenstern616".
Signal vs WhatsApp vs Telegram: which messenger truly protects your privacy? Encryption, metadata and backups compared, plus a step-by-step PGP guide.
Poland launches Operation Horizon: 10,000 troops will guard critical infrastructure, and a new MoD app will let citizens report suspicious activity.
Encryption isn't enough. AI-driven traffic analysis, website fingerprinting and smart networks can unmask VPN and Tor users. Here's what protects you.
On November 18, 2025, Cloudflare went dark for hours. It wasn't a DDoS attack but a database permissions change. Here's the full technical breakdown.
On November 18, 2025, a Cloudflare outage took down X, ChatGPT and Zoom just a month after AWS. Here's what happened and why it matters.
Zero-day vulnerabilities explained: how exploits work, the multimillion-dollar exploit market, Stuxnet and Pegasus, and how to defend in the AI era.
Akira ransomware has extorted over $244M. A joint US, French, German and Dutch advisory reveals new targets (Nutanix) and Cisco, Veeam, VMware flaws.
A major Polish Police overhaul: the Central Cybercrime Bureau (CBZC) merges with the CBŚP to form a new super-unit, the National Investigation Bureau.
Your firewall is no longer enough. Learn why Zero Trust's "never trust, always verify" is becoming the legal and technical standard under NIS2 and DORA.
Traditional security waits for a breach. Threat hunting goes looking for it. Learn why controlled paranoia is the healthiest strategy for your business.
IAM misconfiguration is the leading cause of cloud incidents. Compare AWS, Azure and GCP: shared responsibility, Zero Trust, CMK, CSPM and NIS2.
A practical GDPR security guide: Article 32 controls, DPIA, encryption standards, MFA, backups and the 72-hour breach procedure for CISOs and DPOs.
SOC analysts are drowning in false alarms. Here's how SOAR playbooks and agentic AI cut response times from hours to seconds and help end alert fatigue.
It's not if but when. Build an NIS2-ready incident response plan: 24/72h reporting, CSIRT roles, ransomware playbooks and tabletop exercises.
NIS2 isn't another GDPR. Personal board liability and fines up to PLN 100 million. Find out if your company is covered and how to avoid penalties.
SIEM or XDR? Compare logs vs. telemetry, the true TCO, and see why a hybrid SIEM + XDR model may be the best fit for your SOC in 2025.
After the AWS outage that shook the internet, can the military, healthcare and critical infrastructure trust the cloud? A look at risk and resilience.
A DNS failure in AWS US-EAST-1 on October 20, 2025 took down Slack, Zoom, Fortnite, Coinbase and banks worldwide. Here's what broke and why.
What is OSINT and how do you gather intelligence legally from open sources? Tools, techniques, OPSEC and real cases, from MH17 to business due diligence.
Inside APT28 (Fancy Bear), Russia's GRU Unit 26165: its tactics, tools and biggest operations, from the 2016 US election hack to attacks on Poland.
ISO 27001 certification step by step: the process, real costs (PLN 40k–200k), and 8 key controls to implement. A guide for companies in Poland.
⚠️ The NIS2 deadline passed on October 18, 2024. Non-compliant firms face fines up to EUR 10M. Learn your obligations, deadlines and implementation steps.
A 24/7 in-house SOC needs 5-6 analysts per seat and costs 5x more than you think. Avoid the 4 MSSP selection traps and know your NIS2 board liability.
EDR vs. XDR explained: how each detects and responds to threats, where they differ in scope, and which fits your organization's security strategy.
ESET ranks Poland the world's second most attacked country. We break down why, from ransomware and DDoS to weak passwords and missing MFA.
How AI is fueling phishing, malware and disinformation in 2025, and helping defenders fight back. Key takeaways from the latest ENISA and OpenAI reports.
Is AI eroding our ability to think, write and read deeply? Derek Thompson's warning about the quiet decline of human thinking in the age of ChatGPT.
Japanese brewer Asahi was hit by ransomware that halted production at key plants. What happened, why it matters for supply chains, and how to defend.
BlackCat 3.0 ransomware is hitting companies worldwide with advanced encryption and double extortion. Learn how it works and how to stay protected.
Cl0p exploited an Oracle E-Business Suite zero-day (CVE-2025-61882) to steal corporate data. Oracle's fix is out: patch now and check for compromise.
Poland's energy sector faced 4,000+ cyber incidents in 2024, 4.5% of all attacks nationwide. Experts warn 2025 will be tougher amid hybrid threats.
Poland now tops global cyberattack rankings, with 300+ Russian incidents a day hitting hospitals and water utilities. Warsaw answers with a €1B budget.
A critical new HTTP/2 vulnerability called CONTINUATION Flood enables powerful DDoS attacks that can cripple servers around the world.
Ransomware hits Trans-Europe Express, one of Europe's largest logistics operators, halting operations network-wide and threatening supply chains.
A Spanish e-learning platform was hit by a massive breach exposing data on over 6 million users, now up for sale on a hacker forum.
Ransomware attacks rise for the first time in three years, state-sponsored hackers exploit Cisco firewall zero-days, and VMware ships critical patches.
Europol-coordinated police from 19 countries took down LabHost, one of the world's largest Phishing-as-a-Service platforms, arresting 37 suspects.
Poland fends off 2,000–4,000 cyberattacks every day and neutralizes 99% of them, says Deputy PM and Digital Affairs Minister Krzysztof Gawkowski.
How the WhatsApp zero-click exploit chain worked: CVE-2025-55177 and Apple's CVE-2025-43300 combined to silently install spyware on iPhones.
Ascension, one of the largest US hospital networks, was crippled by ransomware. Now a federal court has allowed a patient class action to proceed.
Foreigners caught filming Warsaw's Gruba Kaśka water intake: a textbook case of reconnaissance that can precede a cyberattack on critical infrastructure.
A nationwide PayTel terminal outage left shoppers across Poland unable to pay by card for hours on Monday, throwing retail and services into chaos.
GitLab patched critical flaw CVE-2025-8243 (CVSS 9.9) that lets attackers run CI/CD pipelines as other users and take over projects. Update now.
Data on millions of VoyageSecure customers, including travel histories and contact details, is for sale on the dark web after a cloud misconfiguration.
Inside the Secret Service takedown of a 100,000-SIM farm near the UN in New York: how SIM boxes work, possible attack scenarios, and who may be behind it.
Card terminals went dark across Poland over the weekend. The operator blames technical issues, but industry insiders point to a possible cyberattack.
A cyberattack on Collins Aerospace's check-in software crippled Heathrow, Berlin and Brussels airports, forcing airlines back to manual check-in.
Google has issued an emergency Chrome update to fix CVE-2025-10585, a V8 zero-day already exploited in attacks. Update your browser now.
An arson attack on high-voltage pylons left over 50,000 Berlin homes and businesses without power. An anarchist group has claimed responsibility.
The EU Data Act has applied since September 12, 2025, giving users control over IoT device data and making it easier to switch cloud providers.
On September 13, an eService payment terminal outage blocked card and BLIK payments across Poland. Officials say it was a technical glitch, not a hack.
September's Patch Tuesday delivers 84 security fixes, including two actively exploited zero-days. Admins should prioritize the critical Windows NTLM flaw.
Unprecedented NPM supply chain attack: 18+ popular packages hijacked, putting over 2 billion weekly downloads at risk. The target: crypto wallets.
The EU Court of Justice ruled that pseudonymized data remains personal data under GDPR when the controller can still re-identify the individuals.
Adobe warns of critical flaw CVE-2025-54236 "SessionReaper," which lets attackers hijack customer accounts on Adobe Commerce and Magento stores.
FastNetMon stopped one of Europe's largest DDoS attacks, peaking at 1.5 billion packets per second from thousands of hijacked IoT devices.
A roundup of the most dangerous vulnerabilities disclosed in the second week of September 2025: priority flaws in Windows, Office, Android and ICS.
ISO 27001 certification in Poland explained: risk management, Statement of Applicability, audit stages, timelines and real 2024–2025 costs in PLN.
Nothing found. Try a different word.
We'd like to use Google Analytics cookies to see how many people visit the site and which content is useful. We'll only set them if you agree. You can change your decision at any time via the “Cookie settings” link in the footer. Cookies Policy