Citrix NetScaler SAML Zero-Day (CVE-2026-88779) Exploited in Attacks: Fixed Versions and Next Steps
CVE-2026-88779 in SAML-enabled NetScaler ADC and Gateway was exploited before a patch. Attackers inject commands via the username field. Patch now.
Vulnerabilities
BeyondTrust and Mandiant disclosed attacks exploiting CVE-2026-102764. Remote Support admins must verify patch BT26-05 and hunt for signs of compromise.
On October 15, BeyondTrust disclosed CVE-2026-102764, a vulnerability in Remote Support that was exploited before it was made public. The vendor and Mandiant confirm intrusions dating back to late August. Patch BT26-05 is available, but applying it is not enough on its own: organizations also need to check whether attackers kept their access.
The flaw comes from insufficient validation of where messages come from in Remote Support’s internal components. It lets an unauthenticated attacker perform file operations on the appliance. Mandiant explains how, after exploiting the flaw, the attackers raised their privileges and set up persistent access.
Researchers attribute the activity to ARMORY CASTLE, a group previously tracked as UNC5221 and suspected of ties to China. They saw the SAWFLY and BARECLAW tools in use, along with log deletion meant to make the intrusions harder to detect. These are the findings of the teams that did the analysis, not a claim made by the attackers themselves.
What’s new is the coordinated disclosure of both the vulnerability and the campaign on October 15. BeyondTrust says the patch was released on October 8, a week before the threat was made public.
The confirmed vulnerability affects Remote Support. The vendor also recommends installing BT26-05 on self-hosted Privileged Remote Access appliances. They share the affected code, although internal testing found no way to exploit the flaw in PRA.
BeyondTrust says cloud-hosted instances of both products were patched automatically. Organizations that run the appliances in their own infrastructure should check the status of their installations. Having the patch in place does not tell you whether a breach already happened.
Remote support systems deserve particular attention because they act as a gateway to other resources across the organization. Incident response can help determine how far a breach reached and plan how to make the environment trustworthy again.
Sources: BeyondTrust, Google Threat Intelligence Group / Mandiant
Read more
CVE-2026-88779 in SAML-enabled NetScaler ADC and Gateway was exploited before a patch. Attackers inject commands via the username field. Patch now.
CVE-2026-104286 (CVSS 9.8) lets unauthenticated attackers write arbitrary files on FortiMail and is actively exploited. See patches and mitigations.
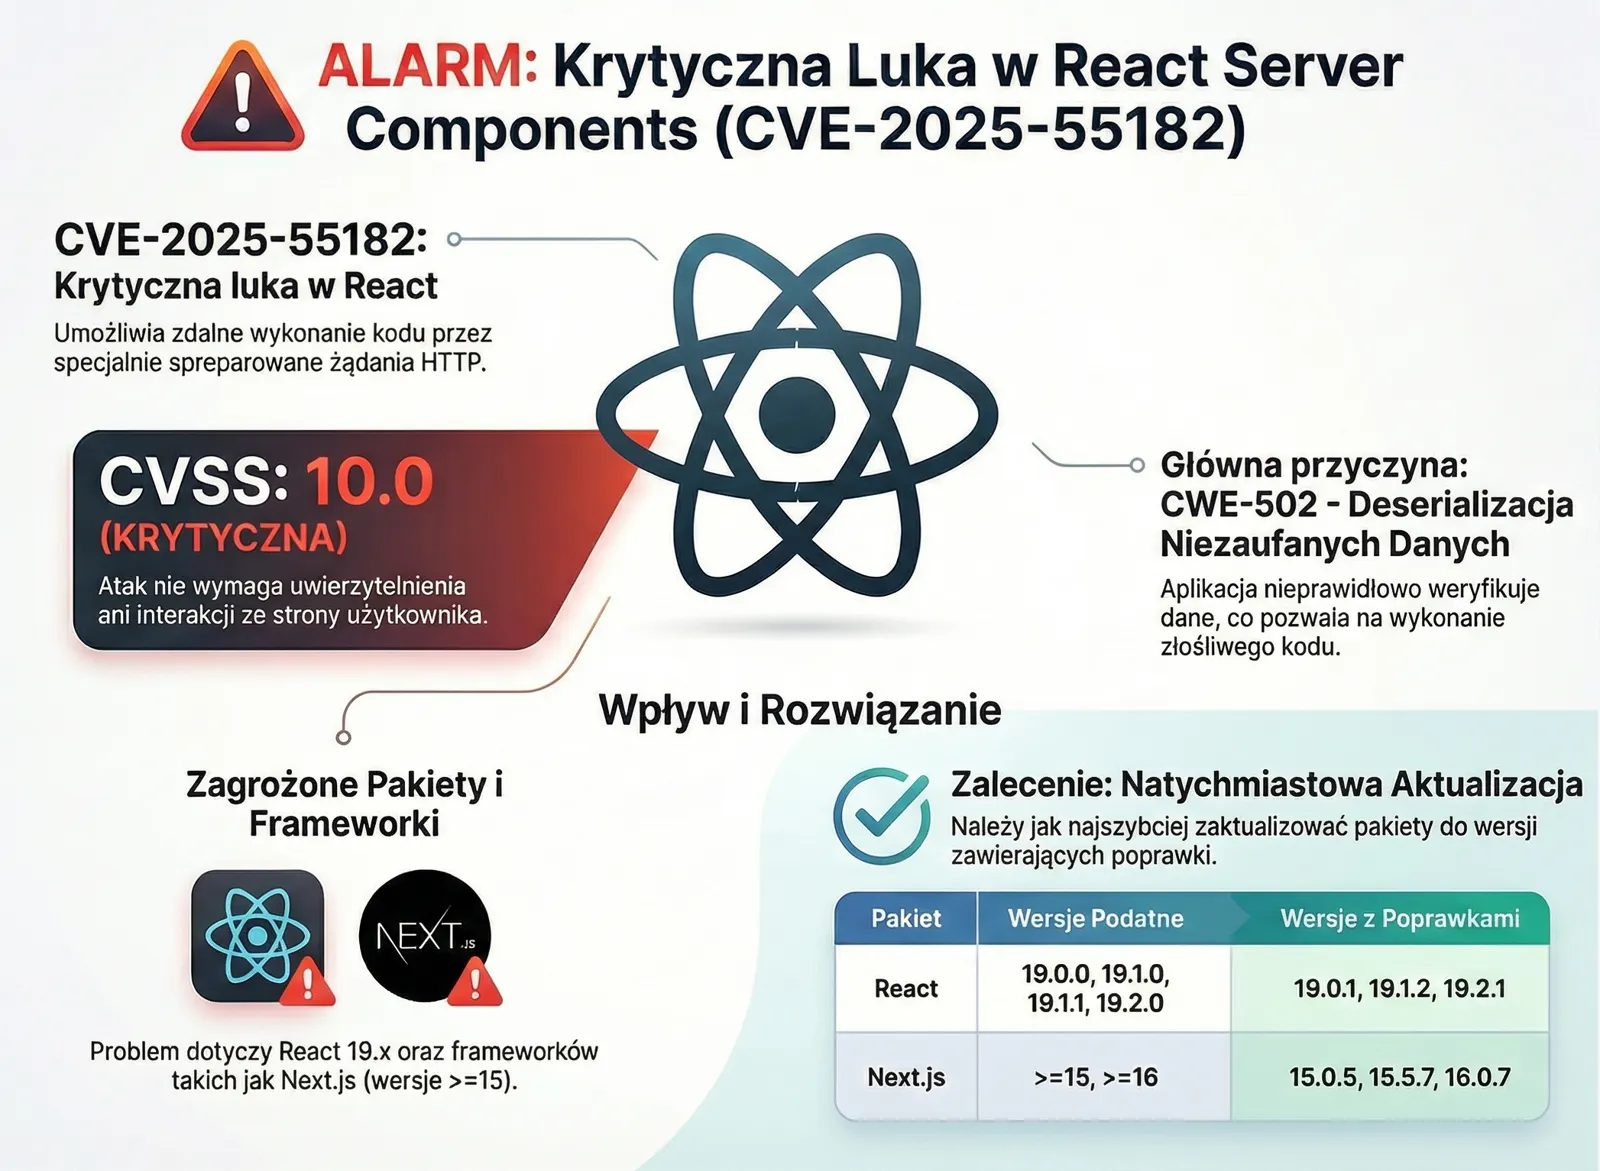
A critical flaw in React Server Components (CVE-2025-55182) enables unauthenticated remote code execution and scored a maximum CVSS 10.0. Patch now.
A free consultation with one of our experts — no obligation, in full confidence.
Let's talkWe'd like to use Google Analytics cookies to see how many people visit the site and which content is useful. We'll only set them if you agree. You can change your decision at any time via the “Cookie settings” link in the footer. Cookies Policy