Bell Financial Group Data Breach: Client Data May Have Been Accessed
Australia's Bell Financial Group confirmed unauthorized access to some of its systems and says a third party may have accessed some client data.
News & analysis
Incidents, vulnerabilities, regulations (NIS2, DORA, KSC) and practical guides — we write about what really changes security for businesses.
Australia's Bell Financial Group confirmed unauthorized access to some of its systems and says a third party may have accessed some client data.
Japanese payment provider Infcurion confirms unauthorized access to Wallet Station, exposing up to 250,000 records. What happened and what to do now.
Broadcom has patched a critical VMware vCenter flaw. Mandiant says the ARMORY CASTLE group exploited it as a zero-day before the update was released.
New PHP releases fix flaws, some of which can lead to remote code execution. Admins should also check the PHP packages their hosting provider ships.
SBC Medical says customer data was taken from its Japanese subsidiary's systems. A separate incident hit clinic accounts in the Tribeau booking service.
Germany's BSI rates the country's cyber situation as tense to critical, citing faster vulnerability exploitation and attackers' growing use of AI.
F5 has fixed five NGINX vulnerabilities. CVE-2026-123007 can trigger a heap buffer overflow in HTTP/2 handling and, in some cases, allow code execution.
Osaki Electric confirms a ransomware attack that encrypted server data, forcing it to halt meter production and shipments. No restart date yet.
CVE-2026-114938 could allow unauthenticated remote code execution on certain x86-64 CPUs. CERT Polska and Red Hat issued warnings on November 17.
A flaw in Optimizely's signup process let an attacker act as an admin on customer accounts and alter scripts served on at least 178 organizations' sites.
Coles is investigating a cybersecurity incident. So far it has found no evidence that customer, employee or supplier data was compromised or exfiltrated.
Nulab confirms unauthorized access to Cacoo exposed about 792 support ticket records, including personal data and, in some cases, last four card digits.
Barracuda says an attacker used ARTEX and a stolen access key left active after a vendor project to breach about ten of its cloud accounts.
The FBI warns Gootloader uses hacked WordPress sites and SEO poisoning to infect organizations, linking it to over $28M in ransom payments.
A cyberattack detected on November 15 has shut the emergency department at Greiz hospital in Germany. Criminal police and prosecutors are investigating.
Stolen credentials let attackers push malicious Claude Code extension versions to Cursor's marketplace and access some of its customer data.
Crypto exchange Unocoin says attackers drained three hot wallets and some customer data may have been exposed. The investigation is ongoing.
A cyberattack on an AI vendor supporting a government startup program exposed names, phone numbers and emails of 20,028 users in South Korea.
An attacker breached a Charles University web application and took data from its student information system. The university is requiring password resets.
Apify confirms an attacker used compromised credentials to access its systems and linked customer accounts. What happened and what users should do now.
Citrix's November 12 bulletins cover 28 flaws in NetScaler ADC and Gateway. CERT-EU urges prompt updates, especially for internet-facing devices.
Huntress details a November 11 campaign abusing ScreenConnect to deploy rogue clients and SCKit. ConnectWise disabled five RMM+ extensions in ~400 partner environments.
On November 12, a Microsoft outage disrupted Outlook, Teams and Exchange Online. What happened and how to limit the impact of similar outages.
Unit 42 details 25 operations in which attackers used the open-source Cairn AI framework against semiconductor, defense and civil society targets.
Intel and AMD released over 50 security advisories covering 200+ flaws in CPUs and software. Most have patches, but not all—here's what admins should do.
Microsoft's November 2026 Patch Tuesday fixes an actively exploited Outlook spoofing flaw (CVE-2026-124194) plus patches for many other products.
On November 10, Adobe issued security updates for nine products, including Connect, Experience Manager, Photoshop and Premiere, fixing about 110 flaws.
SAP's November 2026 Patch Day fixes 35 vulnerabilities, including four rated CVSS 10.0, among them the critical ICM2SHELL and PROXYGATE flaws.
France blames Iran for an October cyberattack on refrigeration systems at 700+ stores, summons Iran's ambassador and pushes for EU sanctions.
N-able took N-central offline and told customers to disconnect on-premises servers while it prepares a fix for 30+ reported vulnerabilities.
CISA added GPUStack flaw CVE-2026-102895 to its KEV catalog. The bug grants admin access without logging in; version 2.2.0 fixes it.
Vanderbilt University is responding to a cyberattack on campus devices and services. BYOD claims data theft, but the university hasn't confirmed it.
France formally attributes October attacks on refrigeration controllers at 700+ retail sites to Iran's Shahid Kaveh unit and seeks new European sanctions.
Italy's foreign minister says G7 ministers will discuss recent cyberattacks in Paris but has no evidence tying them to the Russian government.
Keplr has paused Google and Apple logins after reports of unauthorized transactions. The warning covers some wallets built on Web3Auth infrastructure.
CISA confirms CVE-2026-19868 is being exploited. The SonicWall SSL-VPN flaw affects SAML authentication and can let attackers bypass required MFA.
QNAP is getting reports of NAS break-ins via Plex Media Server. Patch to 1.43.3.10861 now and check any device that was exposed to the internet.
D-Link has issued mitigations for the DGS-3130-30TS switch ahead of a patch, urging admins to disable DDP and restrict management access.
WorkOS says a researcher's AI agent, reportedly outside its test sandbox, pulled sales and support data via an exposed API with leftover dev credentials.
A flaw disclosed Nov. 5 affects certain OpenSSH setups using musl. A fix is out in OpenSSH 10.6p2, and Alpine Linux admins should check their servers.
XLab researchers uncovered CWPdoor, a trojanized Control Web Panel server that runs attacker commands and hides its requests from the access log.
Bitdefender found an Android flaw that triggers a persistent crash loop. A proof-of-concept app needs no permissions and never has to be opened.
Push Security details a campaign using fake OpenAI, SpaceX and Anthropic events and two phishing kits to hijack corporate Microsoft and Google accounts.
Sekoia details an APT29-linked campaign hitting iOS and Android via compromised websites. Updates already available block the documented attack chains.
CISA added CVE-2024-27834 to its Known Exploited Vulnerabilities catalog on November 4. Apple patched the pointer authentication bypass in May 2024.
Cisco disclosed CVE-2026-76506 in the UCS Central management interface. A fix is available; exploitation requires valid credentials on the target system.
Cisco disclosed CVE-2026-76419, an XSS flaw in Unified Communications Manager and SME. Exploitation requires a user to click a link. A fix is available.
OPSSHIELD confirms cPGuard's update channel was hijacked to push a data-stealing script to Linux servers. Patching alone won't revoke stolen credentials.
An attacker accessed Chainstack's customer account database and part of its production environment. Rotate passwords, API keys and node credentials now.
Mozilla released Firefox 159.0.1 to fix high-severity flaw CVE-2026-120572 in page layout. DFN-CERT warns it could allow remote code execution.
Have I Been Pwned has added data from Harvard's November 2025 breach, revealing more than 850,000 unique email addresses. Here's what was exposed.
An overnight cyberattack hit store refrigeration in several European countries. Remote temperature changes forced chains to pull food from sale.
Arara Message breach update: 97 customer-environment servers and about 77 million email addresses at risk. That's addresses, not confirmed individuals.
Japanese beauty site @cosme confirmed a breach exposing about 3 million members' addresses and birth dates. Passwords and card data were not affected.
Attacks hit BTCPay Server 2.4.1 and earlier via a flaw patched in August. Operators of affected instances should rebuild the server and replace wallets.
Ukraine's Air Alert app sent fake nuclear and chemical threat warnings after a breach. Service is partly restored, but use other official channels too.
SmartNews confirmed unauthorized activity in its points and rewards system and paused point exchanges. Impact on user accounts is under investigation.
Russia's Emergency Situations Ministry confirmed hackers used its mobile app to send false alerts, saying the public warning system was not affected.
Update from November 1: Binance has begun a phased restart of withdrawals after a cyberattack. Some networks are back, but platform-wide limits remain.
Cisco Talos details VOLTA, malware that steals passwords, sessions and crypto wallets, then uses AI models to pinpoint a victim's most valuable assets.
JetBrains tools rely on their own certificate trust stores. Fixes are out for IDEs, Toolbox App and jetbrainsd after the eMudhra incident.
Trezor urges CryptoBilis buyers to move funds to a wallet with a new recovery phrase after a credible, still unverified report of a tampered Safe 5.
AO3's operator is investigating a security incident and cannot rule out theft of the account database. Users' works were not deleted, it says.
Red Hat rates CVE-2026-98432, a Linux kernel TCP flaw in IPv4 connection handling, as critical. Here's who is affected and how to check your kernels.
A flaw in AWS Private CA Connector for Kubernetes let users exceed certificate-issuing permissions. Check request configs before you update.
A hijacked third-party JavaScript file enabled unauthorized actions on Polymarket accounts. The platform confirmed the incident and paused trading.
Pluto Security uncovered a campaign abusing code bundled with AI models. Downloads top 32,000, but that doesn't mean 32,000 confirmed infections.
Socket's Searchjacked report links 319 Chrome extensions with 13.4M installs to search hijacking. Here's what admins should check and remove now.
Cisco confirms active exploitation of CVE-2026-76418: a crafted request can reload ASA and FTD firewalls without authentication. Patches are available.
Juniper patched critical flaws in Session Smart Router and Conductor, including CVSS 9.8 bugs enabling unauthenticated command execution and admin access.
WordPress 7.1.4 fixes a flaw allowing code execution during updates, plus stored XSS bugs. Check your site version and patch now.
Attackers are chaining PHP2Shell with Linux kernel flaw CVE-2026-46300 (Fragnesia) to gain root. CISA added it to its exploited vulnerabilities catalog.
CISA warns of four EPICS Base flaws, including possible remote code execution. Update to 7.0.11 and check network access to your control systems.
A new HMICFRS report details breaches at IT suppliers holding UK police data and weak vendor security checks. It doesn't say how many records were stolen.
A US federal court sentenced Artem Stryzhak to 70 months in prison over Nefilim and Hive ransomware attacks hitting healthcare providers and law firms.
CISA advisory ICSA-26-300-02 covers flaws in Mitsubishi Electric and ICONICS. Version 10.97.3 is not enough; three 2026 flaws need ICONICS Suite 10.98.
CERT Polska disclosed boneIO Black flaws allowing unauthenticated command execution from the LAN. Fixed in 1.6.0; older units may need reflashing.
Arctic Wolf analyzed 400+ incidents where attackers posed as IT support in external Microsoft Teams chats to trick employees into granting remote access.
Seoul police uncovered the theft of 8.2 million records from 90+ organizations. Suspects allegedly used AI tools and extorted some of the victims.
Microsoft says its .NET Brotli security fix is still rolling out across Azure Functions. Self-contained apps and custom containers need separate action.
AWS has published a timeline for removing trust in eMudhra certificates. Check CloudFront origin certificates and ALB identity provider certificates now.
GMO CEO Masatoshi Kumagai apologized on Oct. 25, admitting earlier security warnings were handled too slowly, and pledged to cover confirmed fraud losses.
CISA added CVE-2026-110447 in Collabora's built-in CODE server for Nextcloud to its KEV catalog. Admins should update to 26.4.303 now.
A new PHP flaw, CVE-2026-115560, affects an unusual session setup. Until a fix ships, PHP advises disabling file upload progress tracking.
An Oct. 23 analysis shows Node2Shell (CVE-2026-111497) also hits Python's Brotli and brotlicffi packages. Upgrade to Brotli 1.2.1 and brotlicffi 1.2.1.0.
Italy's CSIRT warns of three high-severity flaws in ASUS router firmware 3.0.0.6_102. Find out which update your model needs and what to check now.
Arista confirms active exploitation of CVE-2026-114625 in VeloCloud Orchestrator, letting a read-only user gain operator privileges. Patch now.
Capcom confirms a breach of 11.7 million CAPCOM ID records, exposing emails and login data. Attackers changed passwords on 196 accounts, since reset.
eMudhra's board is ending its global SSL/TLS certificate business after a weak-key incident. What the exit means for customers and how to prepare.
Toronto police have suspended use of Crime Stoppers after new details emerged about a breach at the vendor behind its confidential tip platform.
GitLab issued urgent fixes for CVE-2026-110264, a CVSS 10.0 flaw enabling unauthenticated code execution. Self-managed admins should check versions now.
On October 21, a hijacked LiteLLM release pipeline shipped malicious PyPI packages and container images. Early findings point to stolen GitHub CLI tokens.
Node.js 22.23.4, 24.22.1 and 26.12.1 fix flaws in Brotli decompression, DNS resolution and TLS certificate checks. Update runtimes and containers now.
Rapid7's Q3 2026 report finds high-severity vulnerabilities were exploited three days after disclosure on average. What it means for patching.
PHP has patched two critical flaws, and exploitation attempts are already appearing. Admins should update environments running websites and apps.
The PHP team has warned of two critical flaws rated CVSS 9.2. Patches are due October 21 at 14:00 UTC, so admins should get their updates ready now.
Keys for eight eMudhra intermediate CAs were compromised. Google and Cloudflare detail their response. Admins should review trust stores now.
Horizon3.ai has published an analysis and exploit code for CVE-2026-106173 in FortiSIEM, an unauthenticated RCE flaw. A patch is available.
Oracle's October 2026 Critical Patch Update ships 1,295 security fixes for 1,209 unique CVEs. Admins should review databases, apps and middleware.
Rapid7 details an intrusion chaining two NetScaler flaws. Attackers survived device reboots and stole configuration data and cryptographic material.
Rapid7 disclosed three Eptura Archibus flaws enabling database reads and code execution. Admins should upgrade to version 2025.02 or later.
Pillar Security disclosed an OpenCode flaw affecting Windows and WSL: a malicious MCP server can trigger code execution. Version 1.18.33 fixes it.
Bullhorn has restored regional services after a cyber incident and warns of scammers posing as support staff. Its data investigation is ongoing.
An Idaho school district canceled classes on October 19 after a cyber incident disrupted its network and communications. Authorities are investigating.
ConnectWise disabled seven app identities and suspended Cloud Backup. Admins must check Microsoft 365 for credentials attackers may have left behind.
CISA added CVE-2025-61624 to its KEV catalog on October 16. The flaw lets an authenticated admin write or delete files outside the permitted directory.
BeyondTrust and Mandiant disclosed attacks exploiting CVE-2026-102764. Remote Support admins must verify patch BT26-05 and hunt for signs of compromise.
GreyNoise detailed a proxyjacking campaign that hijacked at least 143 NAS servers and NVRs in 34 countries to resell owners' bandwidth via Pawns.app.
Cisco confirms CVE-2026-76519 is exploited in Secure Email Gateway. A crafted attachment can give root access. Patch and check for compromise.
Palo Alto Networks confirms attacks exploiting CVE-2026-0322, a PAN-OS flaw letting authenticated attackers run code as root. Patch and lock down access.
Ivanti confirms CVE-2026-104935 is exploited in the wild. Researchers detail VPN takeover and credential theft. Patching alone won't rule out a breach.
Microsoft's October updates fix CVE-2026-96951, an actively exploited Windows Shell flaw. Prioritize the patch and verify deployment across your fleet.
Check Point: cyberattacks rose 48% year over year in September 2026 and 61% in Europe, with ransomware up 53%. Key takeaways for businesses.
CyberXero uses 51 AI agents to break into WordPress sites and infrastructure. Poland is its No. 2 target, with 284 government domains scanned.
FBI warns the FortiBleed campaign has hijacked 86,000+ Fortinet FortiGate firewalls and VPNs, passing access to ransomware gangs. 7 steps to take now.
After the MyDr and Medyc data breaches, Poland's government will publicly name companies that fail to secure data. What it means for boards.
Hackers are exploiting CVE-2026-21589 in Jira, Confluence and Bitbucket Data Center to steal crowd.properties credentials. Here's what to do now.
CVE-2026-21589 (CVSS 9.3) affects eight Atlassian Data Center products; Cloud is already patched. Fixed versions and what to do if you can't patch yet.
Attackers hijacked a third-party ASOS messaging platform and pushed a threat to app users. Names and contact details may be exposed. What's the lesson?
Attackers spent 10 days pulling names, addresses and CPR numbers via a partner firm's legitimate access. What it teaches about third-party access risk.
CVE-2026-88779 in SAML-enabled NetScaler ADC and Gateway was exploited before a patch. Attackers inject commands via the username field. Patch now.
Over 600,000 customers and about 6 TB of invoices exposed. The facts on the Fakturownia breach and how to limit the damage, including notifying UODO.
CVE-2026-104286 (CVSS 9.8) lets unauthenticated attackers write arbitrary files on FortiMail and is actively exploited. See patches and mitigations.
Modern LLMs are hitting a memory wall. TurboQuant's vector compression shrinks the KV cache fivefold without sacrificing model intelligence.
litellm, pulled 97M times a month, shipped malware that ran without an import. Only its own bug stopped silent theft of SSH keys and cloud credentials.
Poland's Digital Affairs Minister recommends phone antivirus. We explain what Android antivirus apps can and can't do, and whether you really need one.
A hacker tricked Anthropic's Claude and OpenAI's ChatGPT into helping steal 150 GB of Mexican government data. Here's how the AI jailbreak worked.
Mandatory KSeF is here. Learn how phantom invoices and fake tax office emails target Polish businesses, and how to protect your company from fraud.
Tesla's Mixed-Precision Bridge patent application brings 32-bit AI precision to cheap 8-bit chips. What it means for FSD, Optimus and edge AI.
A complete roundup of the best free, open source penetration testing tools for 2026, from operating systems and web scanners to advanced code analysis.
In-house SOC vs. SOCaaS: costs, TCO and ROI compared, a case study, and NIS2's impact on IT budgets. Why the hybrid model wins in 2026.
A practical guide to SIEM transformation: data normalization, the Pyramid of Pain and Detection as Code. Learn to detect behaviors, not just signatures.
Poland published the mObywatel app's source code, but login walls, right-click blocks and missing backend code turned openness into a facade.
Eight critical Chrome zero-days in one year. How APT groups weaponized the V8 engine, and why the sandbox alone is no longer enough in 2025.
AI isn't only about medicine and convenience. Malicious LLMs like WormGPT and KawaiiGPT are democratizing cybercrime and crafting flawless scams.
Industry 4.0 has ended the era of isolated factories. Learn how IEC 62443 upends traditional thinking about protecting critical infrastructure.
Can AI have trauma? Researchers put ChatGPT, Gemini and Grok through therapy sessions. The result: synthetic psychopathology and a new jailbreak risk.
An analysis of 100 trillion tokens debunks AI myths: roleplay beats office productivity, and users stick to models like Cinderella's glass slipper.
Why did RAM prices skyrocket in 2025? It's not just AI. Inside the silicon physics, Samsung's strategy and the end of Windows 10.
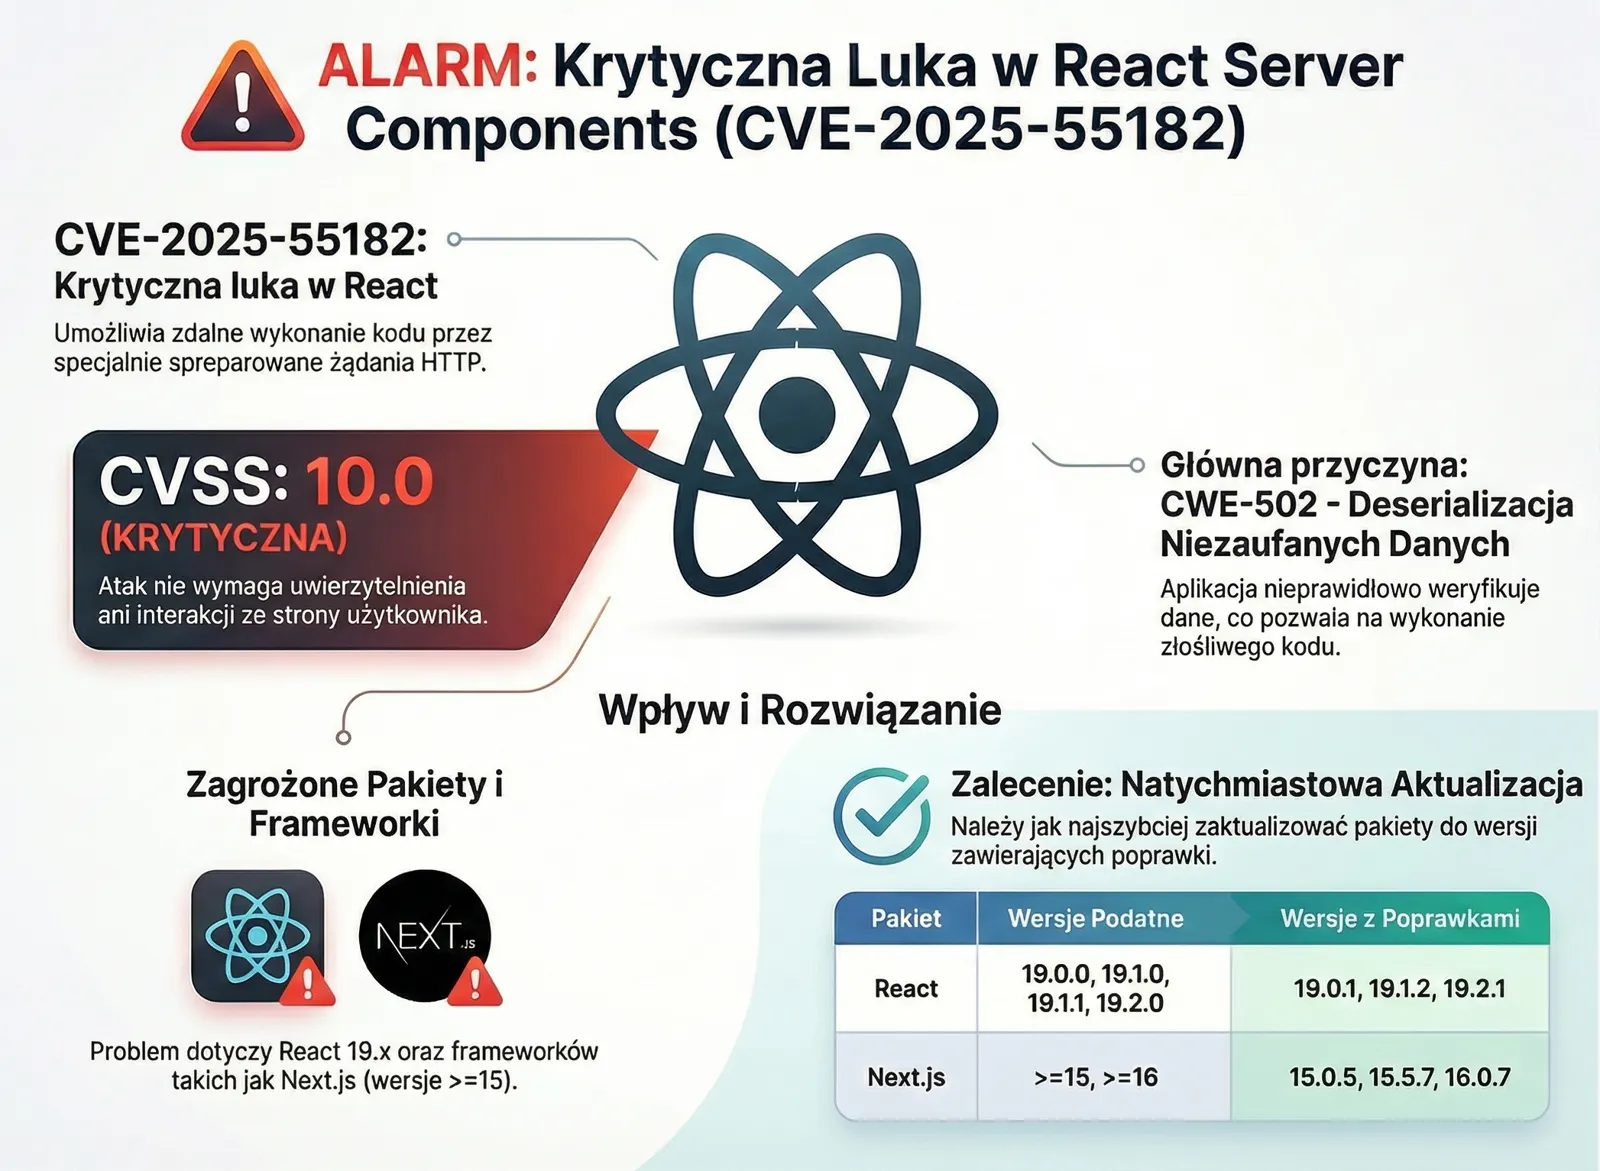
Patched the CVSS 10.0 React2Shell flaw? You're not done. New React Server Components bugs bring DoS and source code exposure to Next.js apps.
Poland's cyber defense has two faces: the new cyber.gov.pl portal with free tools for citizens, and openly acknowledged offensive cyberweapons.
The Dom Development cyberattack exposed PESEL numbers, salaries and children's data. What leaked, what it means, and how to protect yourself now.
Poland plans record spending to fight disinformation in 2026. Inside the government's strategy, from a huge awareness campaign to defending NASK.
Tor is replacing AES-CTR relay encryption with Counter Galois Onion (CGO). What changes, why tagging attacks fail, and where it's 3x faster.
Researchers show how delivery receipts in WhatsApp and Signal let anyone with your number track your screen activity and location and drain your battery.
Running Next.js? React2Shell (CVE-2025-55182) enables remote code execution. Here's how Vercel responded and what you need to patch right now.
Your 2026 guide to the Security Operations Center: team structure, SIEM/XDR/SOAR, NIS2 requirements, deployment models and AI. For CISOs and IT leaders.
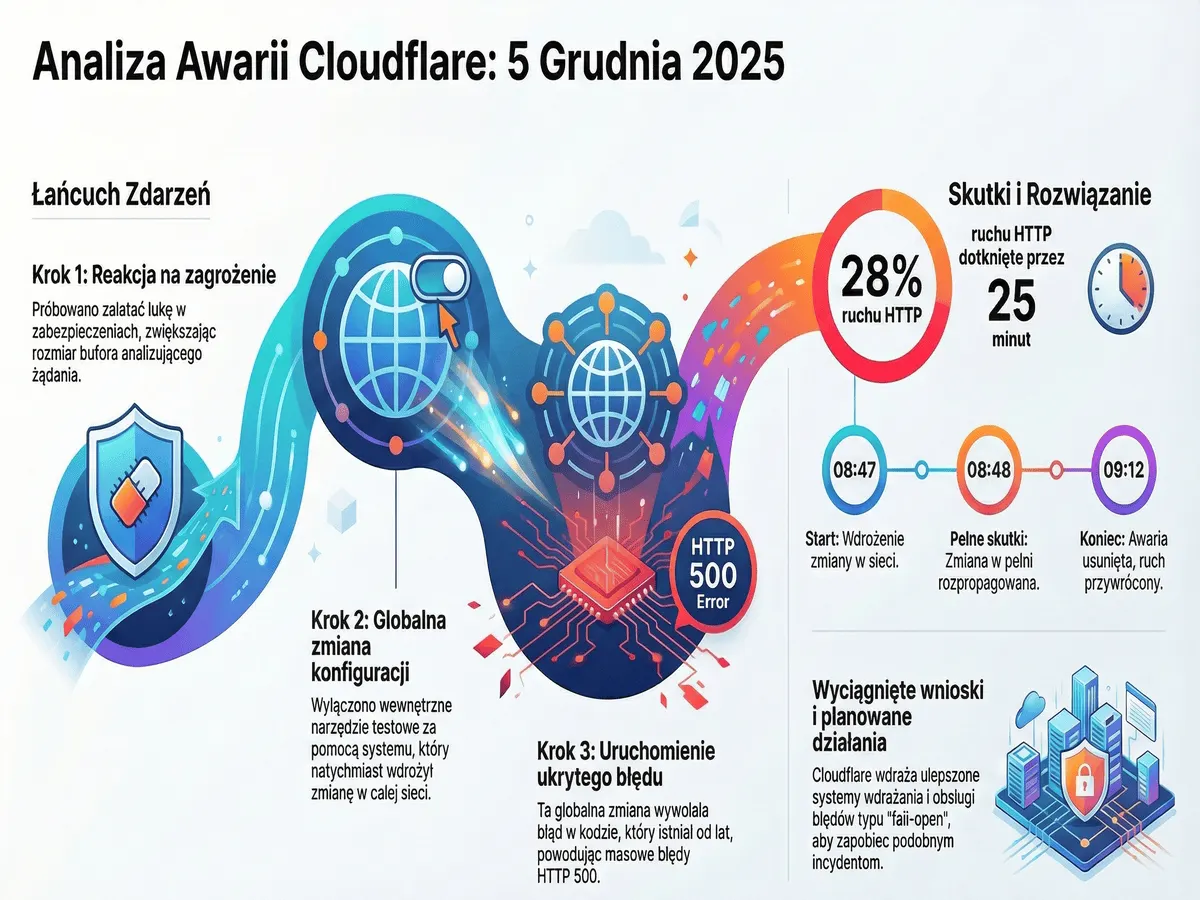
Cloudflare's 25-minute outage on December 5, 2025, explained: a React CVE fix, a WAF buffer change and a fatal Lua nil-value bug.
Agentic AI is rewriting the threat landscape. Learn how Claude Code was weaponized by APT groups like GTG-1002 and why Vibe Hacking matters.
On December 5, Cloudflare stumbled again, taking Zoom and Fortnite down with it. Plus: DownDetectorDownDetector is real, not a meme.
A critical flaw in React Server Components (CVE-2025-55182) enables unauthenticated remote code execution and scored a maximum CVSS 10.0. Patch now.
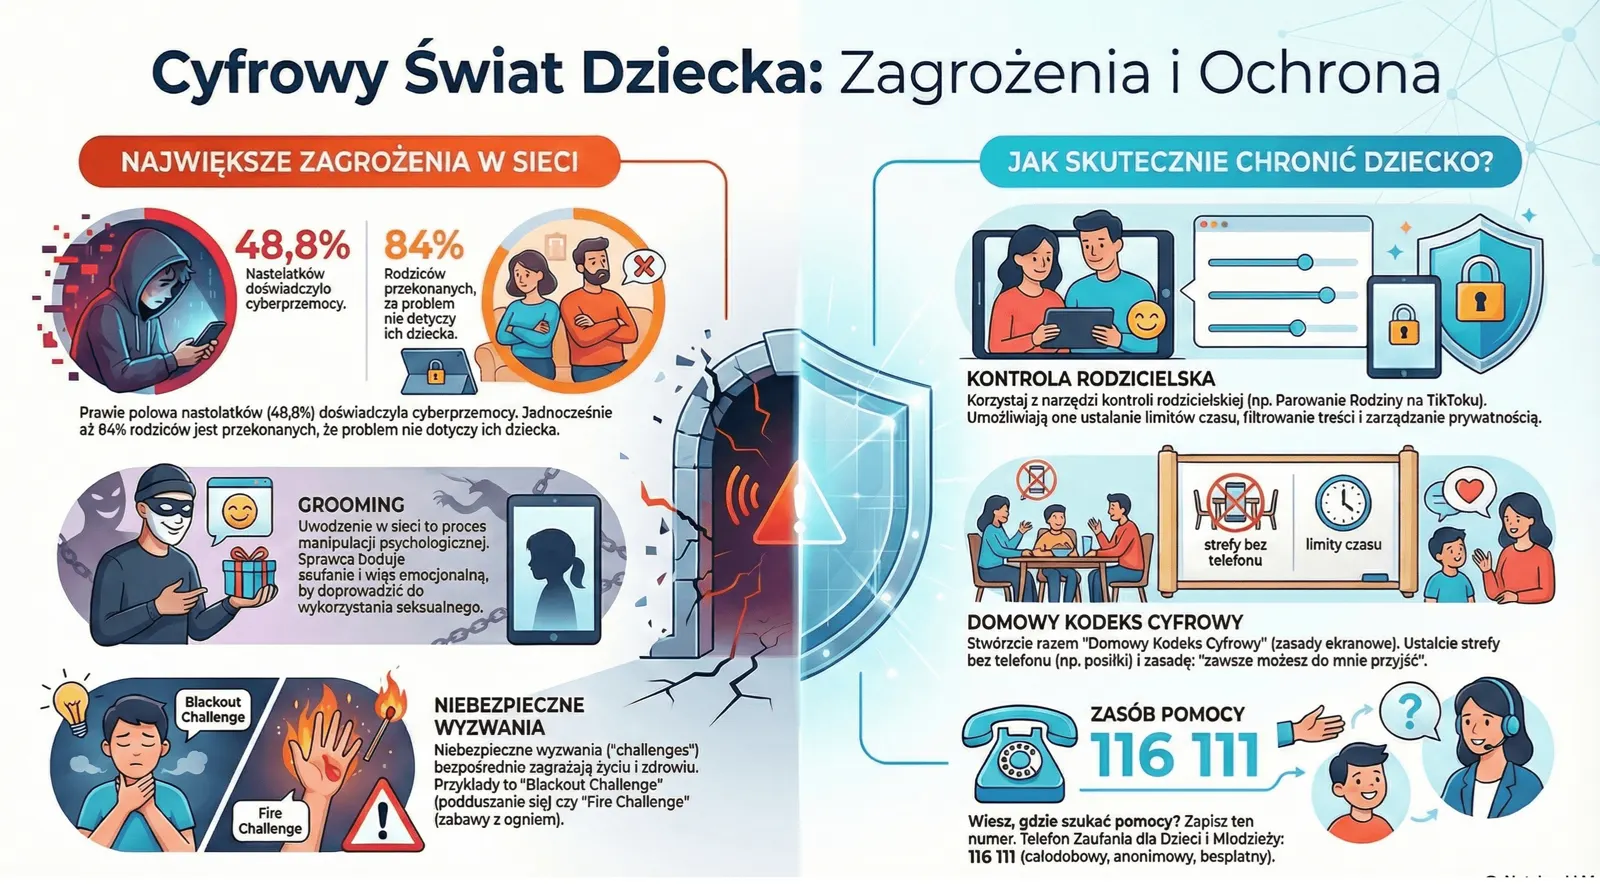
Over 600,000 incident reports. We break down NASK and police data on deadly TikTok challenges, Roblox scams, and Poland's sexting legal trap.
Everyone's feeling the vibe, but nobody reads the code. We look at vibe coding, the rise of slopsquatting, and how AI quietly weakens app security.
75,000 posts, a geolocated window view and... a photo of a dog. See how OSINT techniques unmasked the online hater behind "Morgenstern616".
Signal vs WhatsApp vs Telegram: which messenger truly protects your privacy? Encryption, metadata and backups compared, plus a step-by-step PGP guide.
Poland launches Operation Horizon: 10,000 troops will guard critical infrastructure, and a new MoD app will let citizens report suspicious activity.
Encryption isn't enough. AI-driven traffic analysis, website fingerprinting and smart networks can unmask VPN and Tor users. Here's what protects you.
On November 18, 2025, Cloudflare went dark for hours. It wasn't a DDoS attack but a database permissions change. Here's the full technical breakdown.
On November 18, 2025, a Cloudflare outage took down X, ChatGPT and Zoom just a month after AWS. Here's what happened and why it matters.
Zero-day vulnerabilities explained: how exploits work, the multimillion-dollar exploit market, Stuxnet and Pegasus, and how to defend in the AI era.
Akira ransomware has extorted over $244M. A joint US, French, German and Dutch advisory reveals new targets (Nutanix) and Cisco, Veeam, VMware flaws.
A major Polish Police overhaul: the Central Cybercrime Bureau (CBZC) merges with the CBŚP to form a new super-unit, the National Investigation Bureau.
Your firewall is no longer enough. Learn why Zero Trust's "never trust, always verify" is becoming the legal and technical standard under NIS2 and DORA.
Traditional security waits for a breach. Threat hunting goes looking for it. Learn why controlled paranoia is the healthiest strategy for your business.
IAM misconfiguration is the leading cause of cloud incidents. Compare AWS, Azure and GCP: shared responsibility, Zero Trust, CMK, CSPM and NIS2.
A practical GDPR security guide: Article 32 controls, DPIA, encryption standards, MFA, backups and the 72-hour breach procedure for CISOs and DPOs.
SOC analysts are drowning in false alarms. Here's how SOAR playbooks and agentic AI cut response times from hours to seconds and help end alert fatigue.
It's not if but when. Build an NIS2-ready incident response plan: 24/72h reporting, CSIRT roles, ransomware playbooks and tabletop exercises.
NIS2 isn't another GDPR. Personal board liability and fines up to PLN 100 million. Find out if your company is covered and how to avoid penalties.
SIEM or XDR? Compare logs vs. telemetry, the true TCO, and see why a hybrid SIEM + XDR model may be the best fit for your SOC in 2025.
After the AWS outage that shook the internet, can the military, healthcare and critical infrastructure trust the cloud? A look at risk and resilience.
A DNS failure in AWS US-EAST-1 on October 20, 2025 took down Slack, Zoom, Fortnite, Coinbase and banks worldwide. Here's what broke and why.
What is OSINT and how do you gather intelligence legally from open sources? Tools, techniques, OPSEC and real cases, from MH17 to business due diligence.
Inside APT28 (Fancy Bear), Russia's GRU Unit 26165: its tactics, tools and biggest operations, from the 2016 US election hack to attacks on Poland.
ISO 27001 certification step by step: the process, real costs (PLN 40k–200k), and 8 key controls to implement. A guide for companies in Poland.
⚠️ The NIS2 deadline passed on October 18, 2024. Non-compliant firms face fines up to EUR 10M. Learn your obligations, deadlines and implementation steps.
A 24/7 in-house SOC needs 5-6 analysts per seat and costs 5x more than you think. Avoid the 4 MSSP selection traps and know your NIS2 board liability.
EDR vs. XDR explained: how each detects and responds to threats, where they differ in scope, and which fits your organization's security strategy.
ESET ranks Poland the world's second most attacked country. We break down why, from ransomware and DDoS to weak passwords and missing MFA.
How AI is fueling phishing, malware and disinformation in 2025, and helping defenders fight back. Key takeaways from the latest ENISA and OpenAI reports.
Is AI eroding our ability to think, write and read deeply? Derek Thompson's warning about the quiet decline of human thinking in the age of ChatGPT.
Japanese brewer Asahi was hit by ransomware that halted production at key plants. What happened, why it matters for supply chains, and how to defend.
BlackCat 3.0 ransomware is hitting companies worldwide with advanced encryption and double extortion. Learn how it works and how to stay protected.
Cl0p exploited an Oracle E-Business Suite zero-day (CVE-2025-61882) to steal corporate data. Oracle's fix is out: patch now and check for compromise.
Poland's energy sector faced 4,000+ cyber incidents in 2024, 4.5% of all attacks nationwide. Experts warn 2025 will be tougher amid hybrid threats.
Poland now tops global cyberattack rankings, with 300+ Russian incidents a day hitting hospitals and water utilities. Warsaw answers with a €1B budget.
A critical new HTTP/2 vulnerability called CONTINUATION Flood enables powerful DDoS attacks that can cripple servers around the world.
Ransomware hits Trans-Europe Express, one of Europe's largest logistics operators, halting operations network-wide and threatening supply chains.
A Spanish e-learning platform was hit by a massive breach exposing data on over 6 million users, now up for sale on a hacker forum.
Ransomware attacks rise for the first time in three years, state-sponsored hackers exploit Cisco firewall zero-days, and VMware ships critical patches.
Europol-coordinated police from 19 countries took down LabHost, one of the world's largest Phishing-as-a-Service platforms, arresting 37 suspects.
Poland fends off 2,000–4,000 cyberattacks every day and neutralizes 99% of them, says Deputy PM and Digital Affairs Minister Krzysztof Gawkowski.
How the WhatsApp zero-click exploit chain worked: CVE-2025-55177 and Apple's CVE-2025-43300 combined to silently install spyware on iPhones.
Ascension, one of the largest US hospital networks, was crippled by ransomware. Now a federal court has allowed a patient class action to proceed.
Foreigners caught filming Warsaw's Gruba Kaśka water intake: a textbook case of reconnaissance that can precede a cyberattack on critical infrastructure.
A nationwide PayTel terminal outage left shoppers across Poland unable to pay by card for hours on Monday, throwing retail and services into chaos.
GitLab patched critical flaw CVE-2025-8243 (CVSS 9.9) that lets attackers run CI/CD pipelines as other users and take over projects. Update now.
Data on millions of VoyageSecure customers, including travel histories and contact details, is for sale on the dark web after a cloud misconfiguration.
Inside the Secret Service takedown of a 100,000-SIM farm near the UN in New York: how SIM boxes work, possible attack scenarios, and who may be behind it.
Card terminals went dark across Poland over the weekend. The operator blames technical issues, but industry insiders point to a possible cyberattack.
A cyberattack on Collins Aerospace's check-in software crippled Heathrow, Berlin and Brussels airports, forcing airlines back to manual check-in.
Google has issued an emergency Chrome update to fix CVE-2025-10585, a V8 zero-day already exploited in attacks. Update your browser now.
An arson attack on high-voltage pylons left over 50,000 Berlin homes and businesses without power. An anarchist group has claimed responsibility.
The EU Data Act has applied since September 12, 2025, giving users control over IoT device data and making it easier to switch cloud providers.
On September 13, an eService payment terminal outage blocked card and BLIK payments across Poland. Officials say it was a technical glitch, not a hack.
September's Patch Tuesday delivers 84 security fixes, including two actively exploited zero-days. Admins should prioritize the critical Windows NTLM flaw.
Unprecedented NPM supply chain attack: 18+ popular packages hijacked, putting over 2 billion weekly downloads at risk. The target: crypto wallets.
The EU Court of Justice ruled that pseudonymized data remains personal data under GDPR when the controller can still re-identify the individuals.
Adobe warns of critical flaw CVE-2025-54236 "SessionReaper," which lets attackers hijack customer accounts on Adobe Commerce and Magento stores.
FastNetMon stopped one of Europe's largest DDoS attacks, peaking at 1.5 billion packets per second from thousands of hijacked IoT devices.
A roundup of the most dangerous vulnerabilities disclosed in the second week of September 2025: priority flaws in Windows, Office, Android and ICS.
ISO 27001 certification in Poland explained: risk management, Statement of Applicability, audit stages, timelines and real 2024–2025 costs in PLN.
Nothing found. Try a different word.
We'd like to use Google Analytics cookies to see how many people visit the site and which content is useful. We'll only set them if you agree. You can change your decision at any time via the “Cookie settings” link in the footer. Cookies Policy