Fake OpenAI and SpaceX Event Invites Used to Hijack Corporate Microsoft and Google Accounts
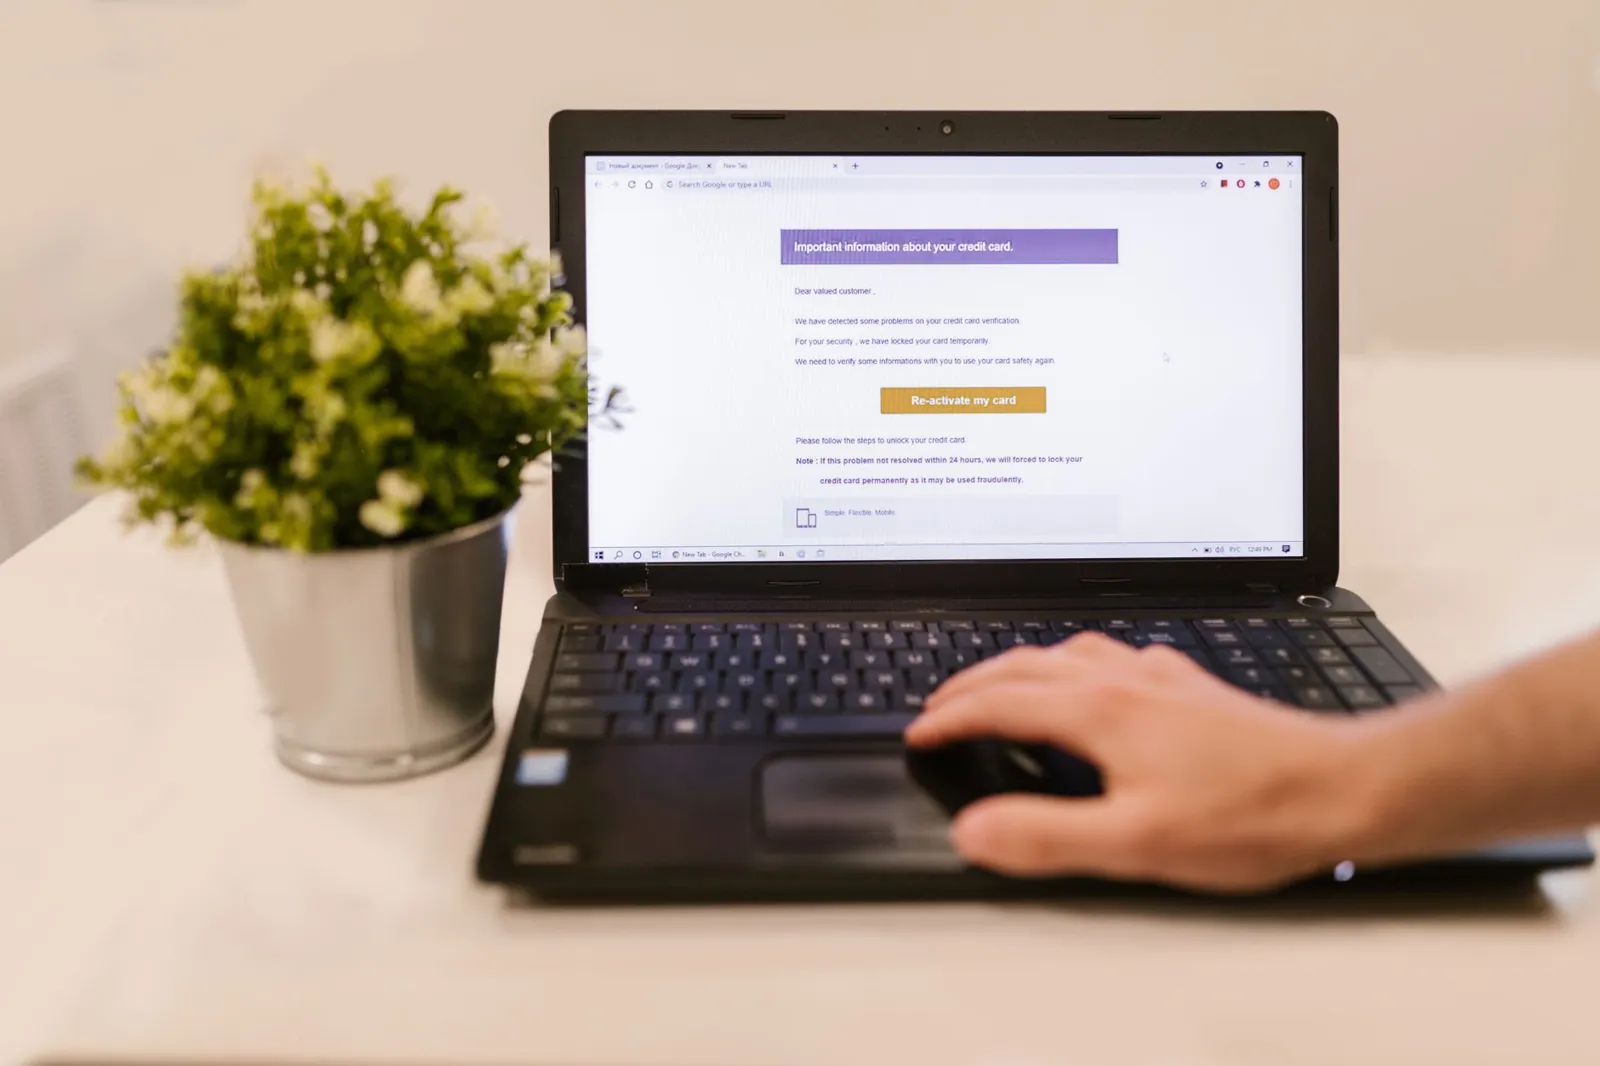
Push Security details a campaign using fake OpenAI, SpaceX and Anthropic events and two phishing kits to hijack corporate Microsoft and Google accounts.
We test the most common way into a company — its people.
A social engineering test is a safe simulation of an attack that targets people rather than systems. We check whether employees recognise fake emails, phone calls and attempts to enter the office, and show how to reduce that risk.
A report with results and recommendations and, on request, employee training based on what actually worked in the test.
See also: NIS2, DORA and ISO 27001 compliance audits, which require staff training.
FAQ
Yes. We agree the scope, scenarios and timing with management beforehand. We don't take over real accounts, don't collect passwords and don't disclose individual results unless you want us to.
Phone fraud: the criminal pretends to be IT support, a bank or the CEO to obtain data or a money transfer. Our tests check whether employees recognise such attempts.
A report with the results (e.g. how many people clicked and how many reported the attempt), a description of weak points in procedures, and training recommendations.
News
Push Security details a campaign using fake OpenAI, SpaceX and Anthropic events and two phishing kits to hijack corporate Microsoft and Google accounts.
Have I Been Pwned has added data from Harvard's November 2025 breach, revealing more than 850,000 unique email addresses. Here's what was exposed.
Arara Message breach update: 97 customer-environment servers and about 77 million email addresses at risk. That's addresses, not confirmed individuals.
Leave us a message and a dedicated advisor will get in touch with you.
Contact usWe'd like to use Google Analytics cookies to see how many people visit the site and which content is useful. We'll only set them if you agree. You can change your decision at any time via the “Cookie settings” link in the footer. Cookies Policy